CtrlOps 1.0
Your server. Audited, managed, and deployed with AI.
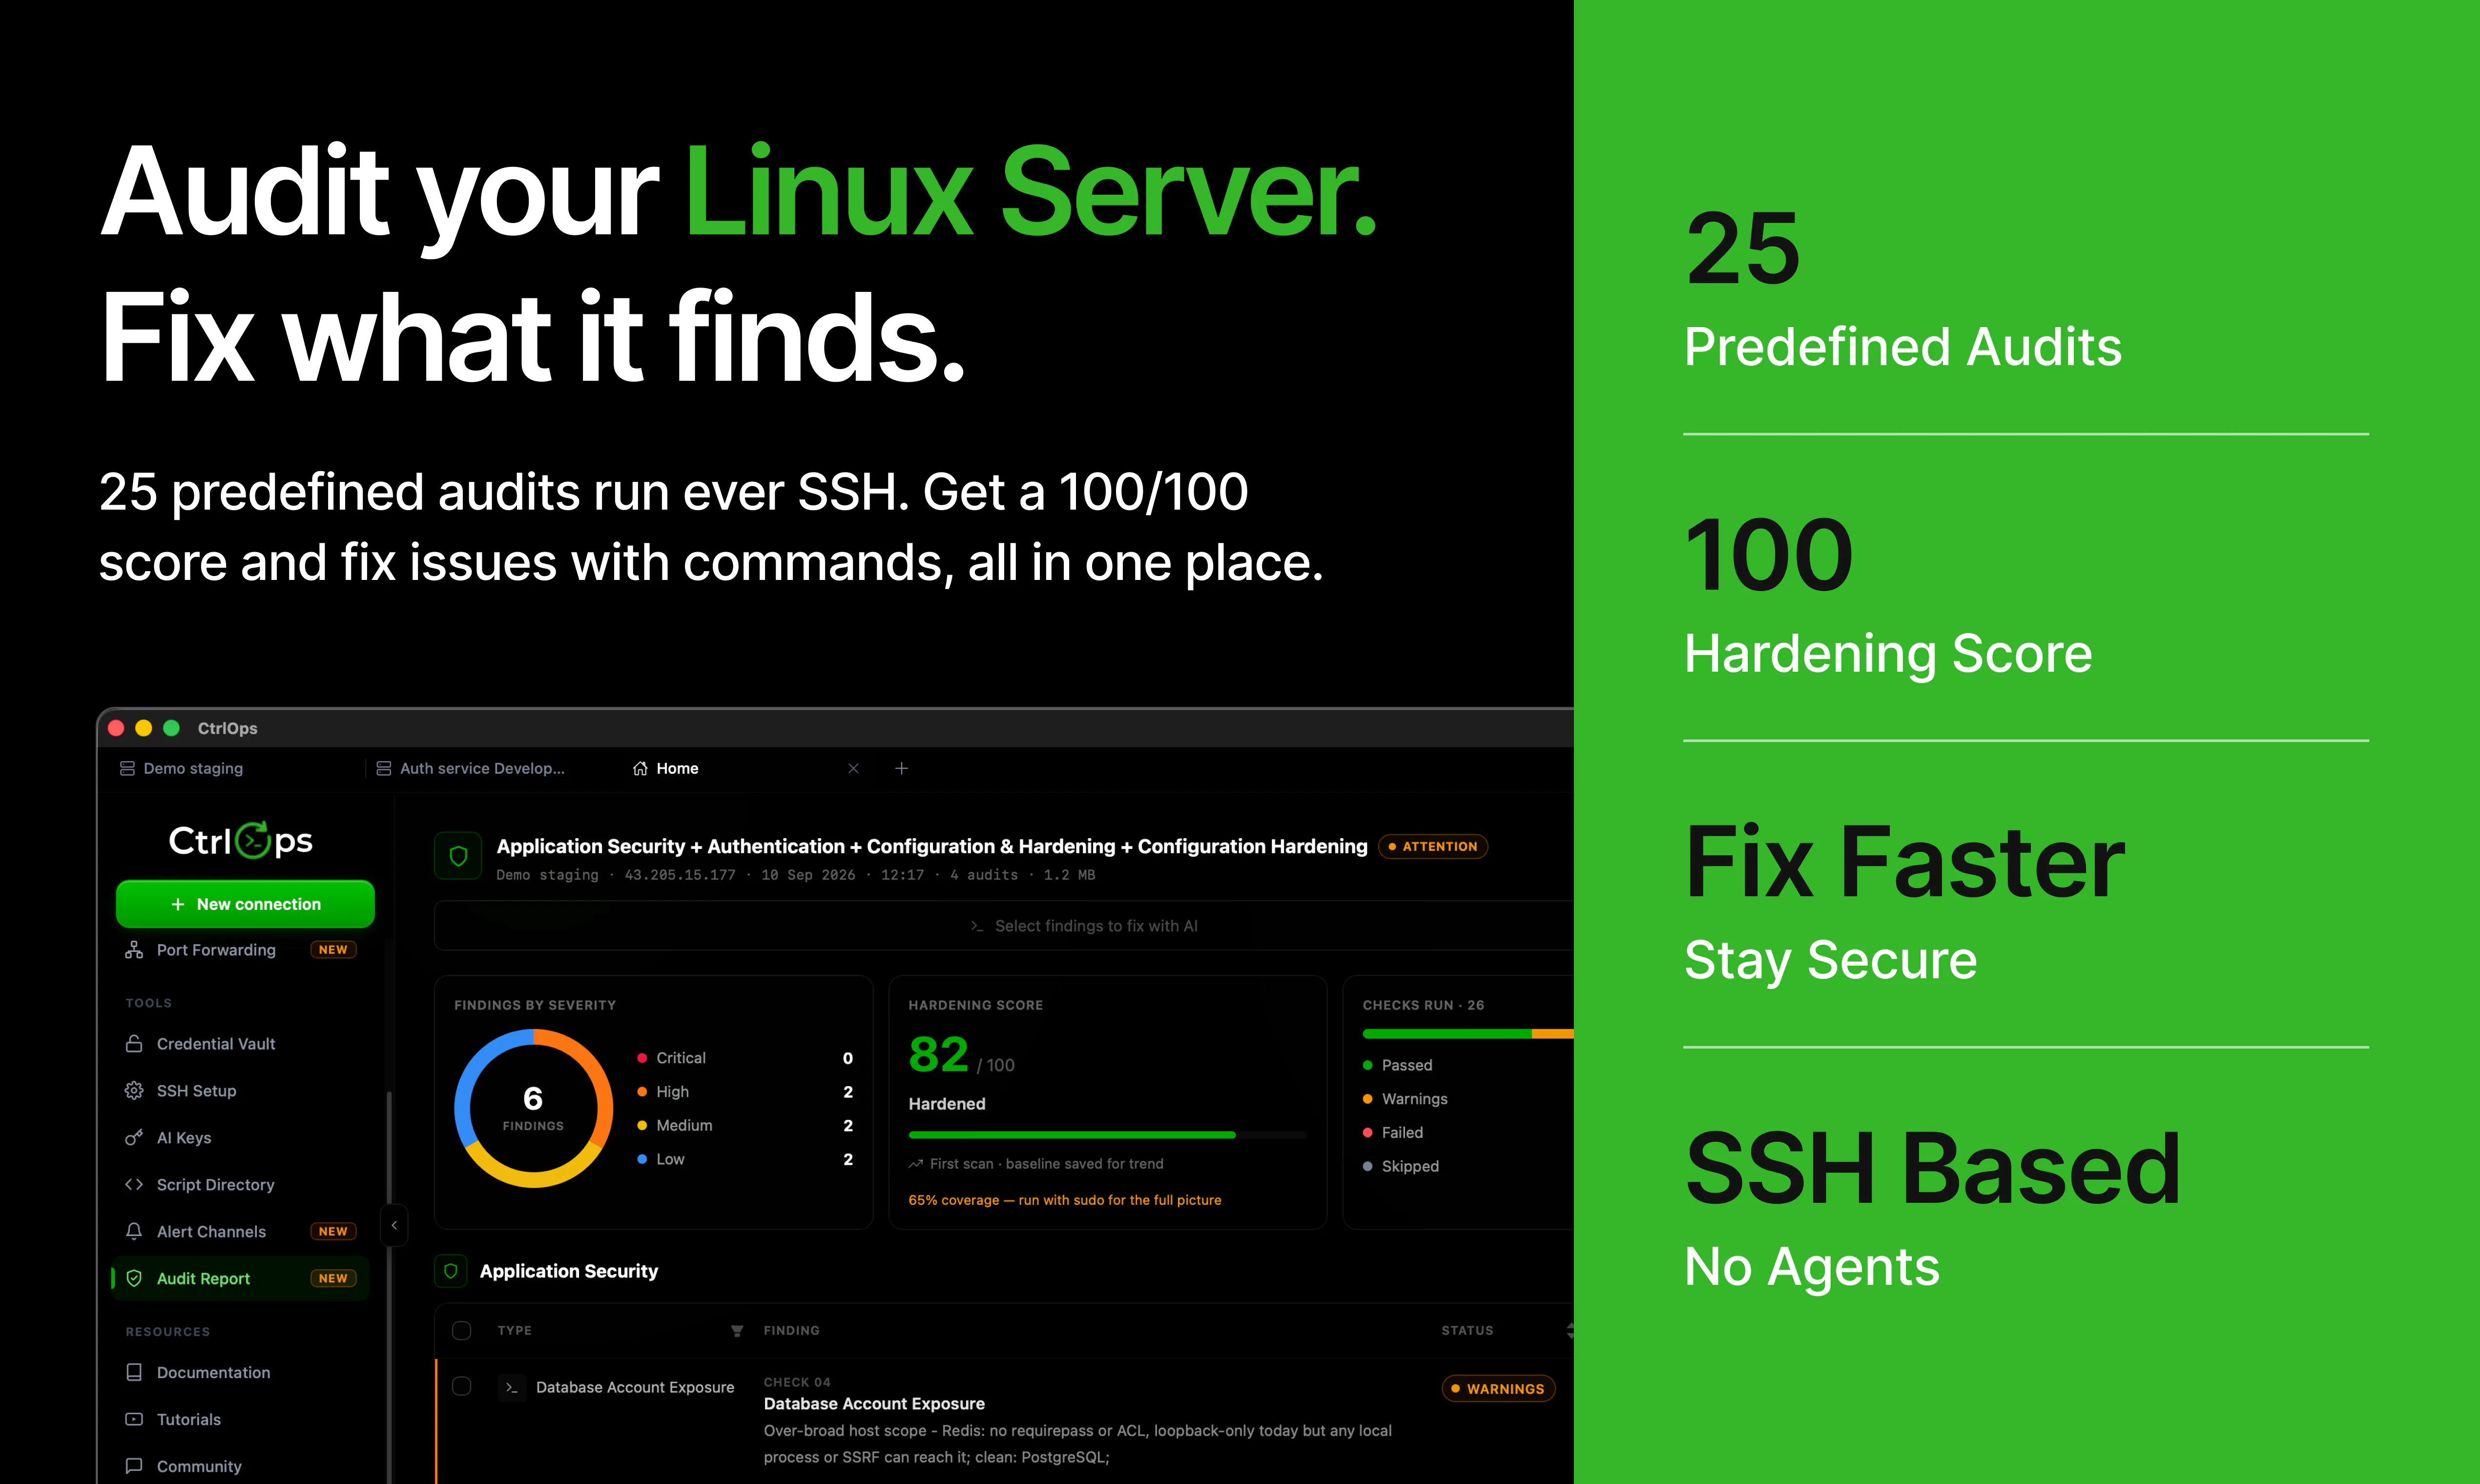
Do you actually know who has access to your servers right now? CtrlOps gives you a security hardening score across 25 checks, a PDF audit report, and fix commands for every issue found. See who can log into every server, revoke access from your whole fleet in one click, and assign any level of roles/access without touching the terminal. Every log file, found and searchable without SSH. Deploy any app from GitHub in minutes. 100% local. Your credentials never leave your machine.
AI Analysis
CtrlOps is a 100% local, AI-powered platform for Linux server auditing, management, and deployment. Core features include a security hardening score from 25 checks, PDF audit reports with fix commands, fleet-wide visibility into logins and access (one-click revoke, role assignment without terminal), searchable logs without SSH, and rapid GitHub-based app deployment. It solves critical pain points like unknown server access risks, tedious manual security audits, terminal dependency, and inefficient log analysis. The USP is its privacy-first local execution (credentials never leave the machine), AI automation, and all-in-one simplicity. Overall value proposition: empowers developers and admins with secure, efficient server operations without cloud dependency or complex setups.
In 2025-2026, with AI adoption maturing in DevOps, rising cybersecurity threats, increasing demand for privacy-focused local tools amid data breach concerns, and shift towards automated security compliance, the timing is highly favorable. Economic pressures push for efficiency gains without heavy cloud costs. Excellent Timing.
Technical difficulty is medium-high due to AI accuracy for security checks and local LLM integration, but the product is already launched indicating viability. Development costs moderate for a focused tool; low supply chain risk as pure software; compliance risks exist for security features but mitigated by local design. Strong scalability for server fleets and good team fit for dev tools. Overall rating: High.
Main segments: DevOps engineers, SREs, sysadmins, and security teams (ages 25-45, tech-savvy) in startups, SMEs, and tech firms managing Linux infrastructure. Industries: software development, IT services, cybersecurity. Geographic: primarily North America and Europe. TAM for DevSecOps ~$15B+, SAM for Linux server tools ~$2B, SOM ~$150M for AI-local niche. Core pains: access opacity and manual ops. High willingness to pay for time-saving, risk-reducing tools (likely freemium/subscription).
Medium. Direct competitors: 1. Teleport (goteleport.com) - secure access and auditing. 2. JumpCloud (jumpcloud.com) - directory and server management. 3. Ansible (ansible.com) - automation and deployment. 4. Lynis (github.com/CISOfy/lynis) - open-source security auditing. 5. Fleet (fleetdm.com) - device/server management. Advantages: unique AI-driven insights, full local/privacy focus, all-in-one (audit/access/logs/deploy) with one-click simplicity and PDF reports. Disadvantages: newer entrant may lack enterprise maturity, integrations, or proven scale compared to established players; pricing not detailed but local model could be a differentiator.
Upgrade Pro to unlock full AI analysis
Similar Products
Auriko
Trading desk for LLM calls
▲ 332 votes
React UI Kit V7
All the chat components you need. None of the complexity
▲ 115 votes
Replay QA Security Scan
Automated Penetration Testing for AI-Built Apps
▲ 102 votes
CodeBurn
See where your AI coding spend actually goes
▲ 101 votes
Refoid
Automate App Store refund responses and track every outcome
▲ 68 votes
Opaline
PostHog for team Claude Code and Codex sessions.
▲ 0 votes