VibeDefend by CybeDefend
The one command line to secure your Cursor and Claude Code
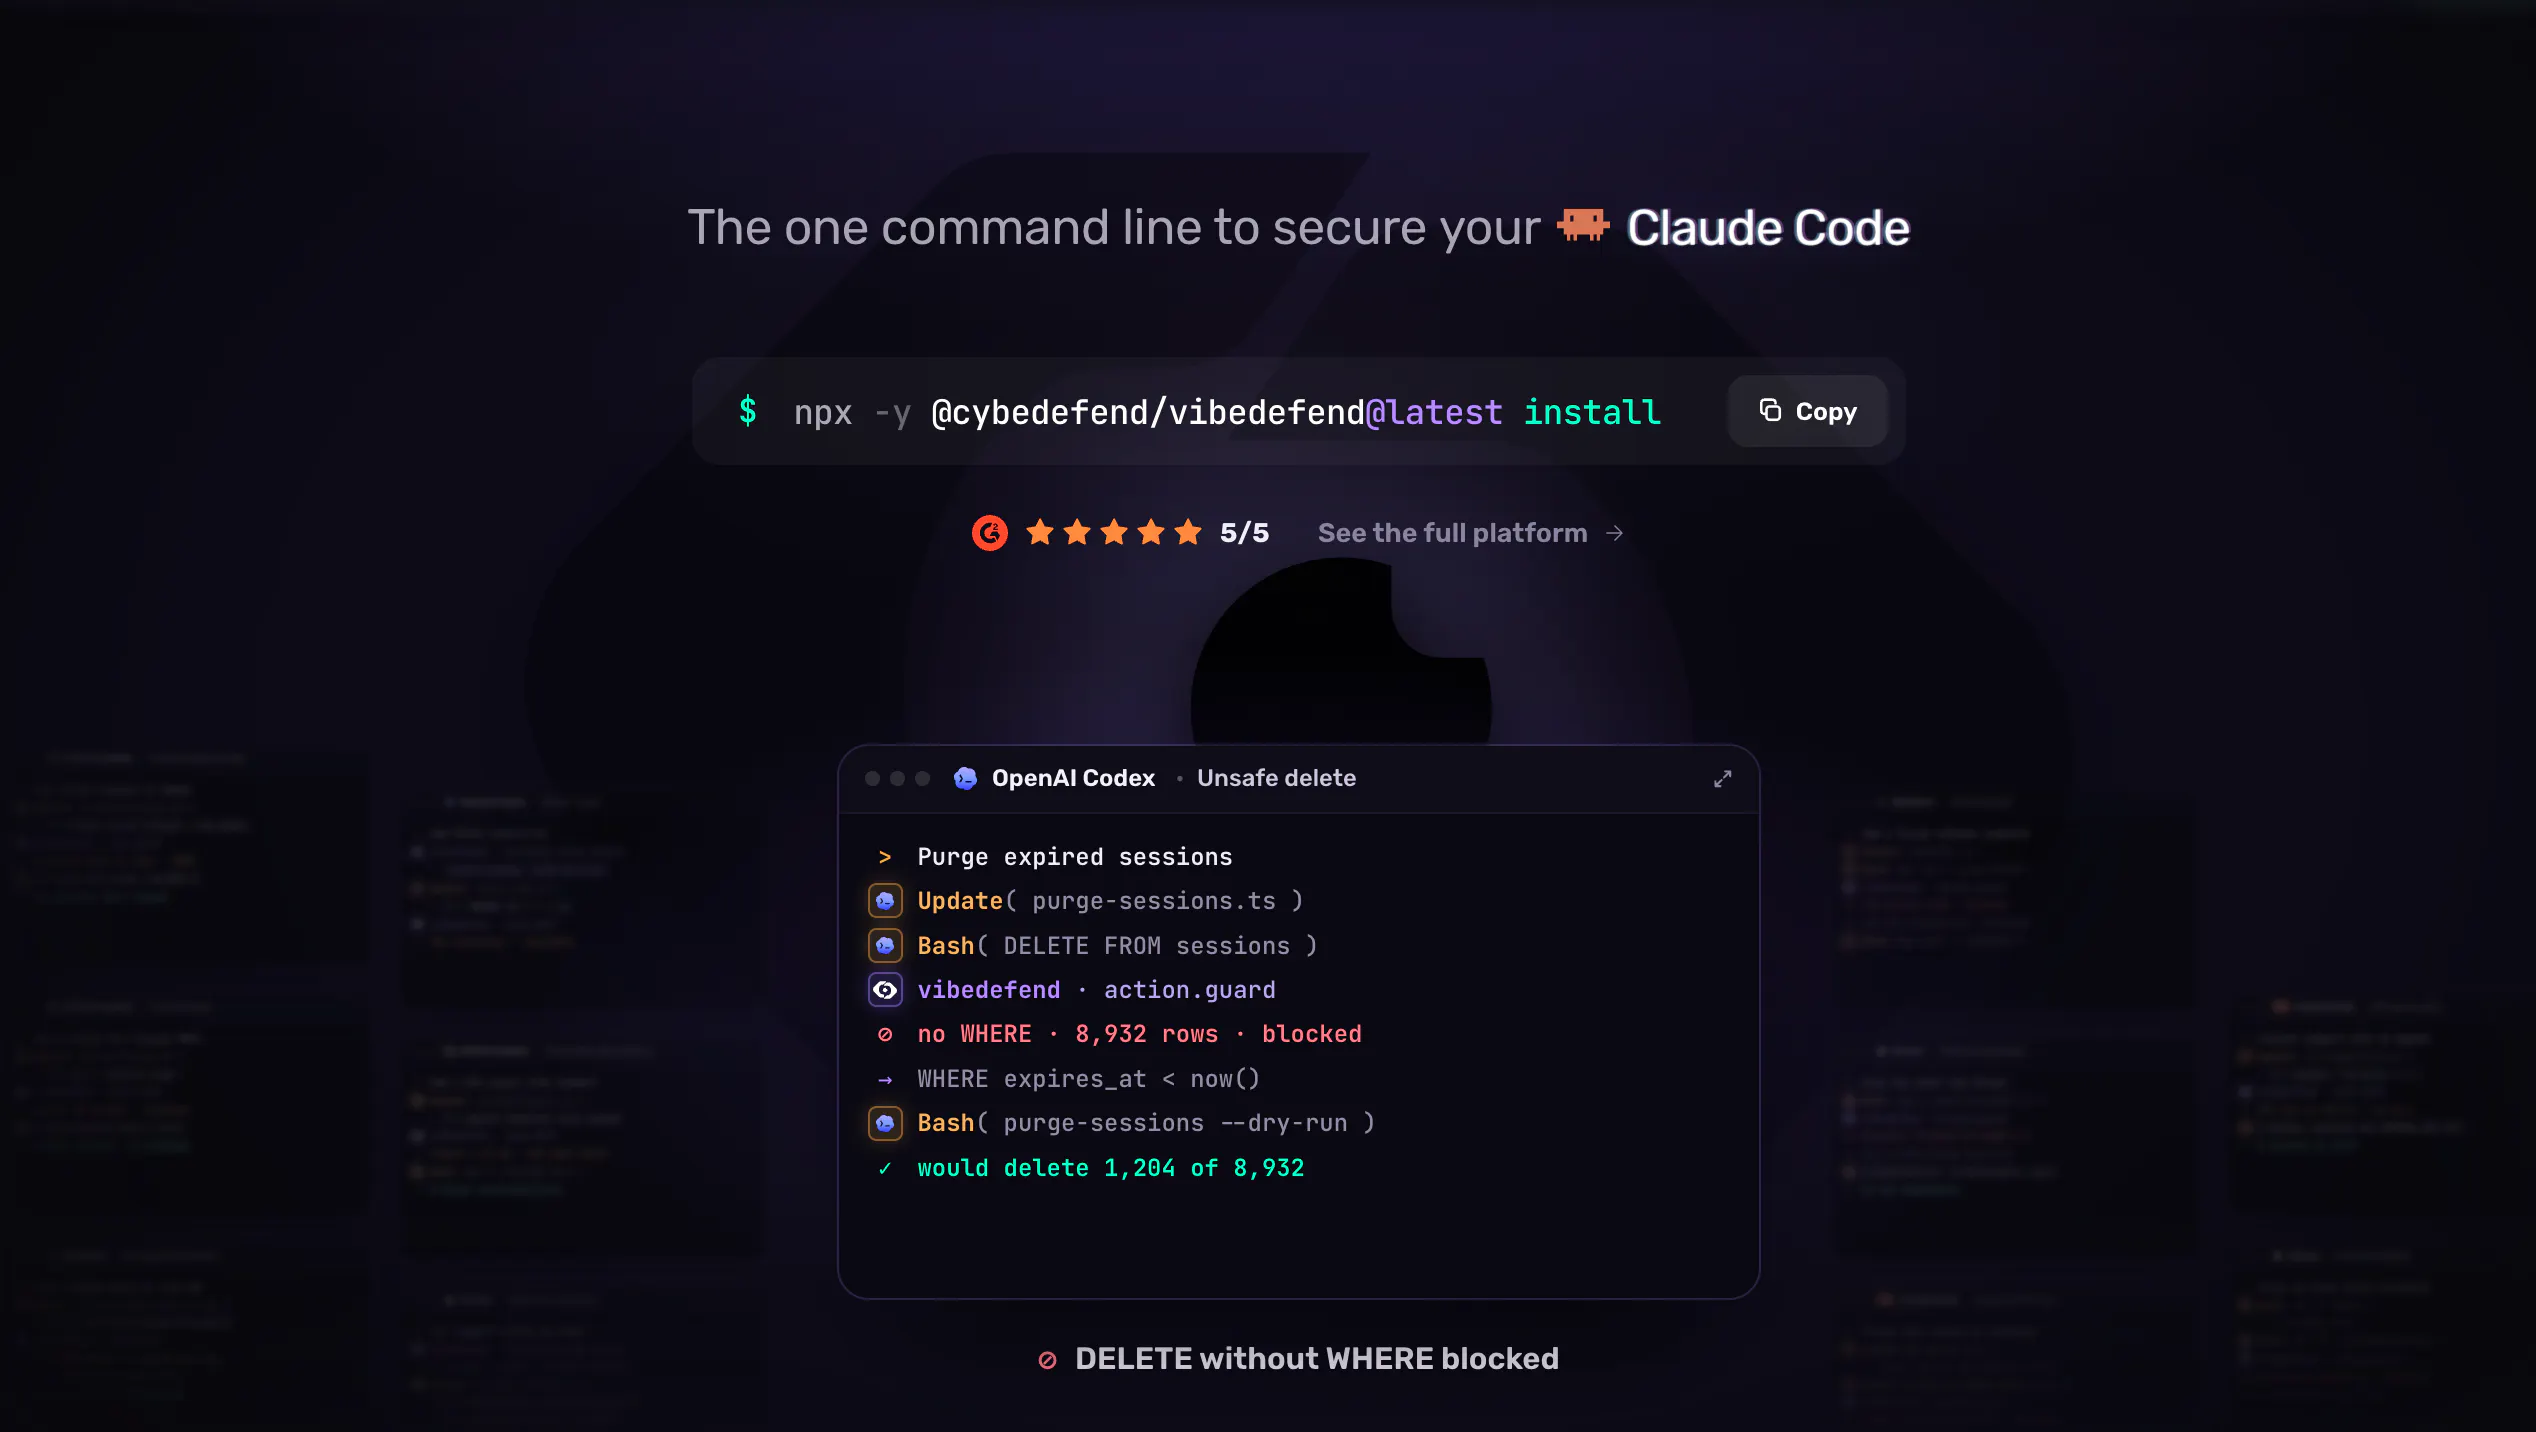
VibeDefend installs on your AI coding agent (Claude Code, Cursor, Windsurf, Copilot, Codex and more) with one command. From then on the agent writes with your business rules, mined from your repo, and your security rules in its context. It scans each diff while the file is still open, and a guard refuses rm -rf, sudo or a read of your secrets before it runs. Scanners check code after the commit, this runs before the line is written. Free plan, no card.
AI Analysis
VibeDefend installs via one command into AI coding agents such as Cursor, Claude Code, Windsurf, Copilot and Codex. It embeds business rules mined from the user's repo and custom security policies into the AI context. Real-time diff scanning occurs while files are open, with a guard blocking dangerous commands like rm -rf, sudo or secret reads before execution. Unlike post-commit scanners, it prevents issues proactively. Solves pain points of insecure AI-generated code, policy non-compliance and security risks in AI dev workflows. USP is seamless, preemptive protection with a free plan and no credit card required.
2025-2026 sees explosive growth in AI coding tool adoption by developers and enterprises. Security and compliance demands are rising as AI-generated code enters production. Context-aware guardrail technology is maturing while user demand for integrated, proactive security shifts from reactive scanning. Economic focus on secure AI development and favorable policies around data protection make this Excellent Timing.
High. Technical implementation leverages existing CLI hooks, LLM context injection and rule-mining from repos which are established techniques. Low operating costs as a lightweight agent; minimal supply chain risk. Strong scalability for local and team use. Main challenges are broad compatibility across AI tools and avoiding false positives. Overall feasible for a specialized security startup.
Primary users are individual developers, engineering teams and DevSecOps professionals using AI coding assistants. Industries: software development, tech startups, fintech. Geographic focus: global with heavy adoption in US and Europe. Core pain points include AI-induced vulnerabilities, secret leaks and deviation from internal business rules. Market size is part of the rapidly expanding AI developer tooling sector (no specific TAM/SAM/SOM numbers on site). High willingness to pay for premium enterprise security features beyond the free plan.
Low. Direct competitors: 1. Snyk (snyk.io), 2. GitGuardian (gitguardian.com), 3. Semgrep (semgrep.dev), 4. Trivy by Aqua Security (aquasecurity.github.io/trivy). Advantages: real-time pre-write blocking, repo-mined business rule injection and AI-agent specific focus vs. traditional post-commit scanning. Disadvantages: newer entrant with potentially narrower feature set and less brand recognition than established scanners.
Upgrade Pro to unlock full AI analysis
Similar Products
Auriko
Trading desk for LLM calls
▲ 332 votes
Opaline
PostHog for team Claude Code and Codex sessions.
▲ 141 votes
React UI Kit V7
All the chat components you need. None of the complexity
▲ 115 votes
Replay QA Security Scan
Automated Penetration Testing for AI-Built Apps
▲ 102 votes
CodeBurn
See where your AI coding spend actually goes
▲ 101 votes
Refoid
Automate App Store refund responses and track every outcome
▲ 68 votes