Polylane for Security
Catch exploitable vulnerabilities before they ship
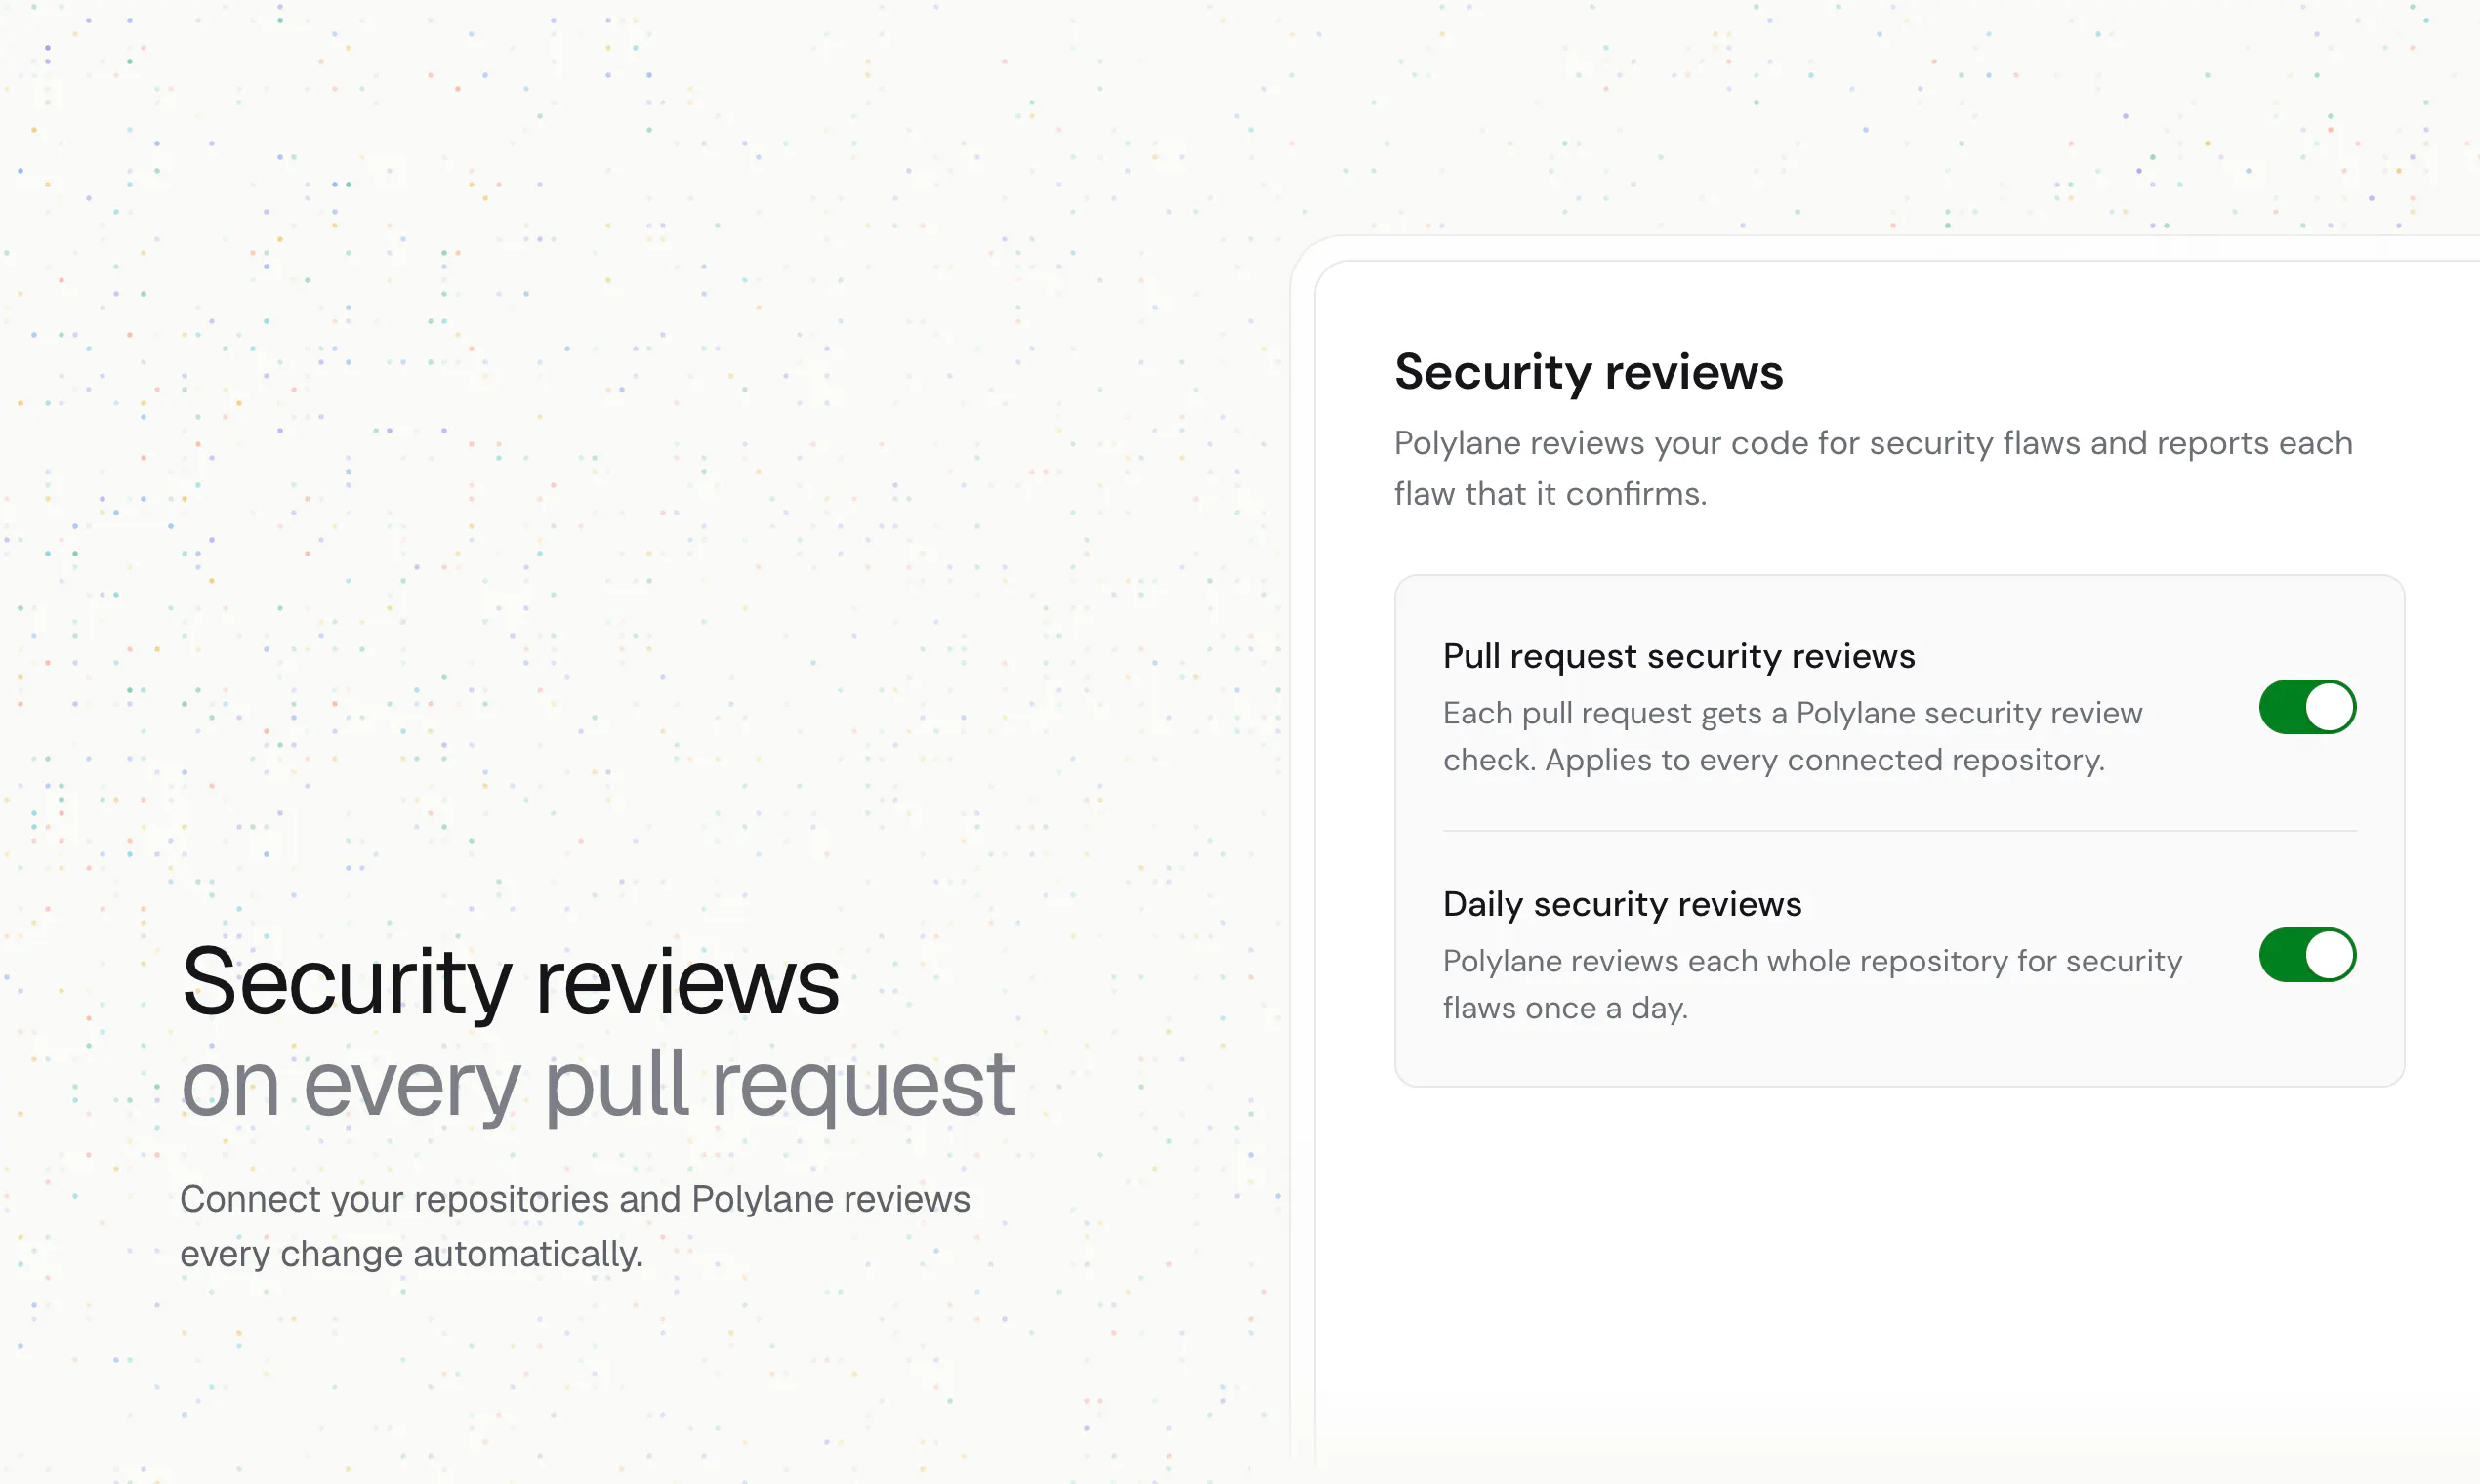
Polylane reviews production-bound pull requests for exploitable security flaws. Findings trace attacker-controlled input to the vulnerable line, with the evidence and suggested fix. Safe candidates are ruled out with a reason. Daily dependency scans find known CVEs, prioritise the most severe and open fix pull requests on active, deployed repositories.
AI Analysis
AI analysis not yet available for this product.
Similar Products
Cohere Parse 5
Turn complex docs, tables & images into AI-ready data
▲ 158 votes
Adapt
The company brain that gets work done
▲ 124 votes
Replay QA Security Scan
Automated Penetration Testing for AI-Built Apps
▲ 102 votes
WikiFix for Confluence
Find and fix issues in your knowledge base
▲ 86 votes
Audryo
Customer email your agent can operate.
▲ 68 votes
Refoid
Automate App Store refund responses and track every outcome
▲ 68 votes